
Tag: IAM
-

The Terrifying Truth About User Access on Your Systems
Ask any CISO where their biggest identity-related blind spot is, and you’ll rarely hear “onboarding.” It’s everything that comes after. Most organizations have figured out how to grant access when someone joins. But the middle of the identity lifecycle—the transfers, promotions, contract extensions, and tool sprawl—is where governance breaks down and risk silently accumulates. By the…
-
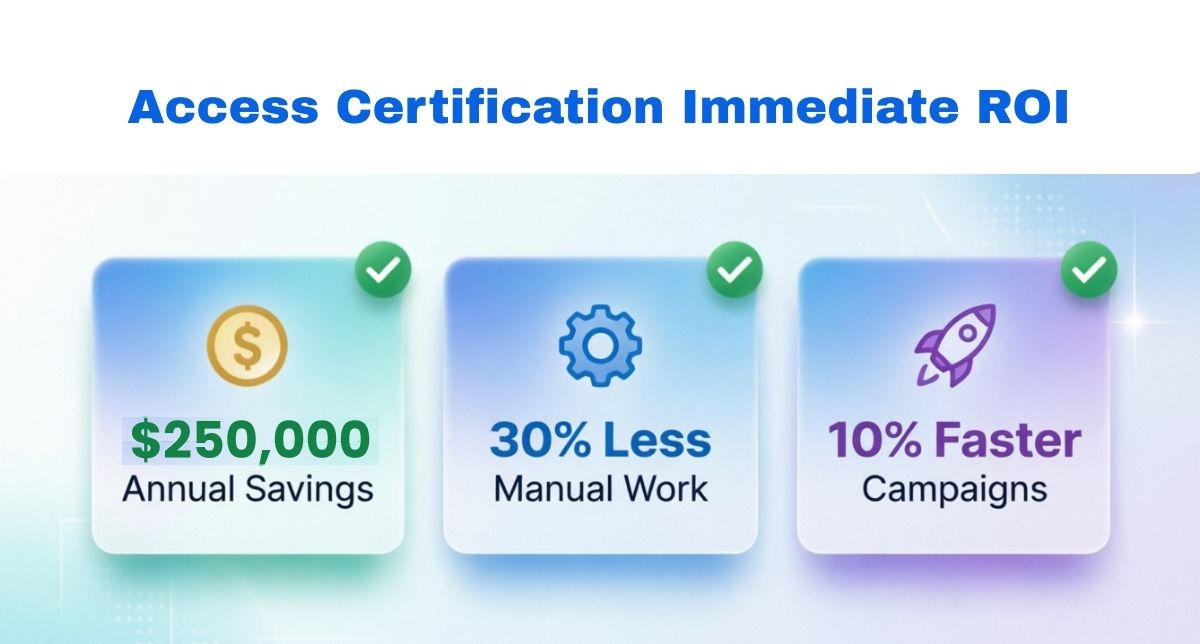
How Replacing Smartsheet Saved One Company $250k on Access Certification
For many growing fintech and enterprise organizations, access certifications become a compliance bottleneck long before they become a security solution. What begins as a simple workflow quickly evolves into a complex process involving thousands of employees, hundreds of reviewers, and strict regulatory deadlines. When the process is built on tools that weren’t designed for identity…
-
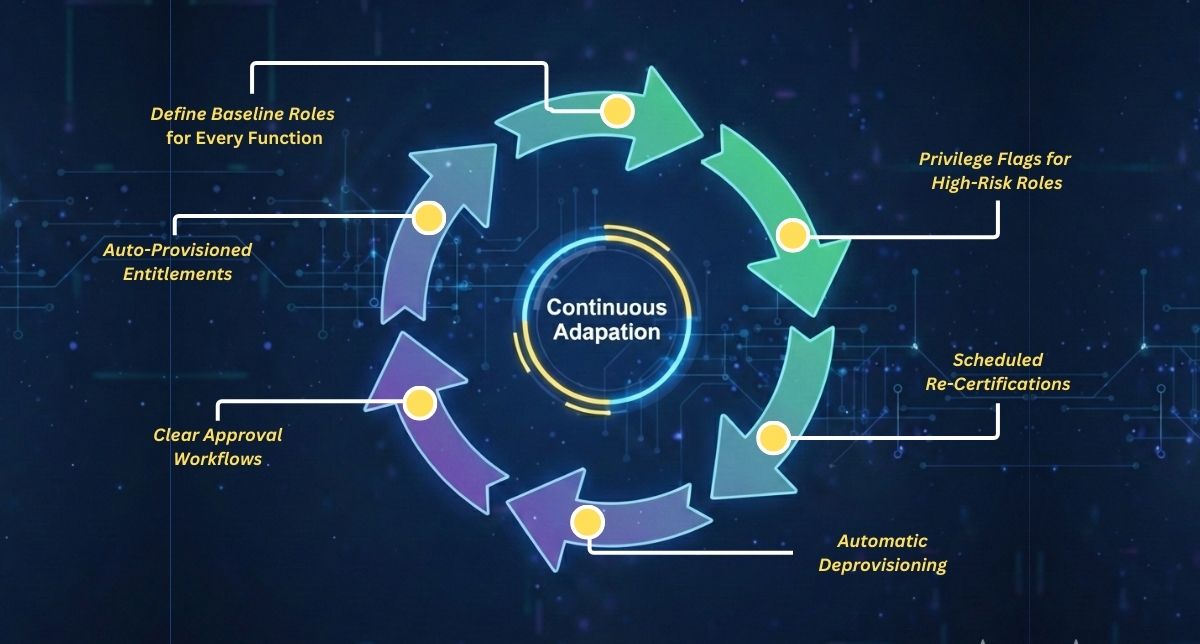
From Static to Scalable: Building an RBAC System That Grows With Your Cloud Stack
Is your Role-Based Access Control (RBAC) struggling to keep up with your cloud growth? Discover the six pillars of a scalable, adaptive identity model that turns access management into a business enabler. Many teams treat Role-Based Access Control (RBAC) as a classic “set it and forget it” project. The common scenario: define a handful of…
-
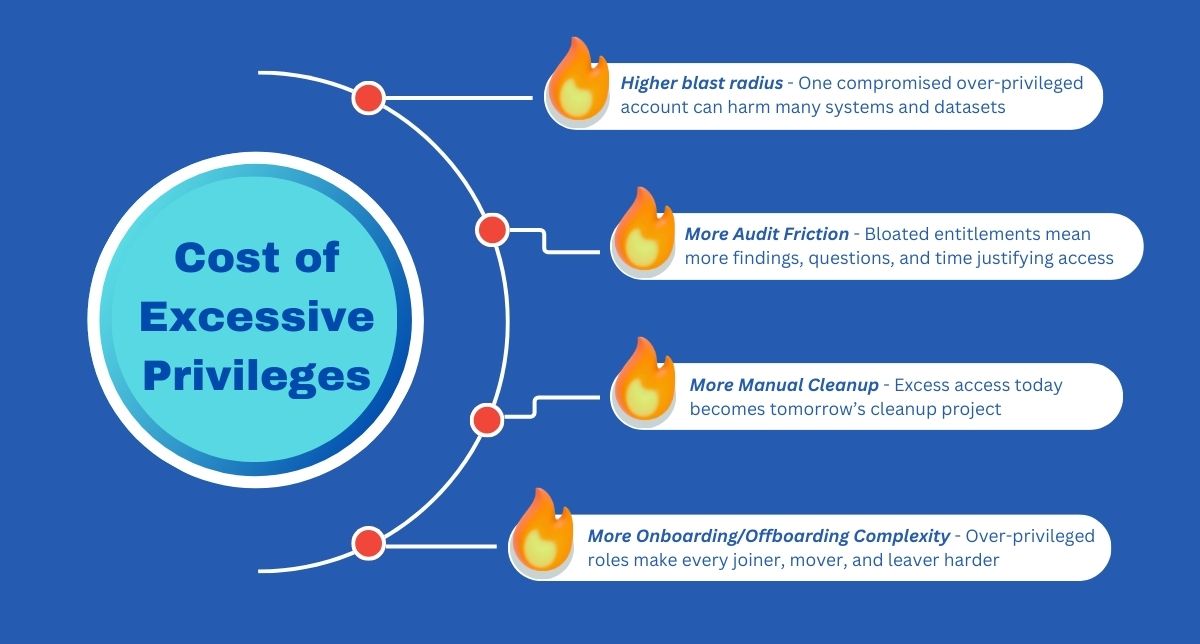
The Silent Tax: Why Excessive Privileges Cost More Than Just Security Risk
Over-permissioned users aren’t just a security problem. Discover the hidden operational costs of excessive privileges—from audit friction to onboarding delays—and why least privilege is a business efficiency imperative. We talk about the principle of “least privilege” almost exclusively as a security imperative—and for good reason. Limiting access shrinks the blast radius of a potential breach.…
-
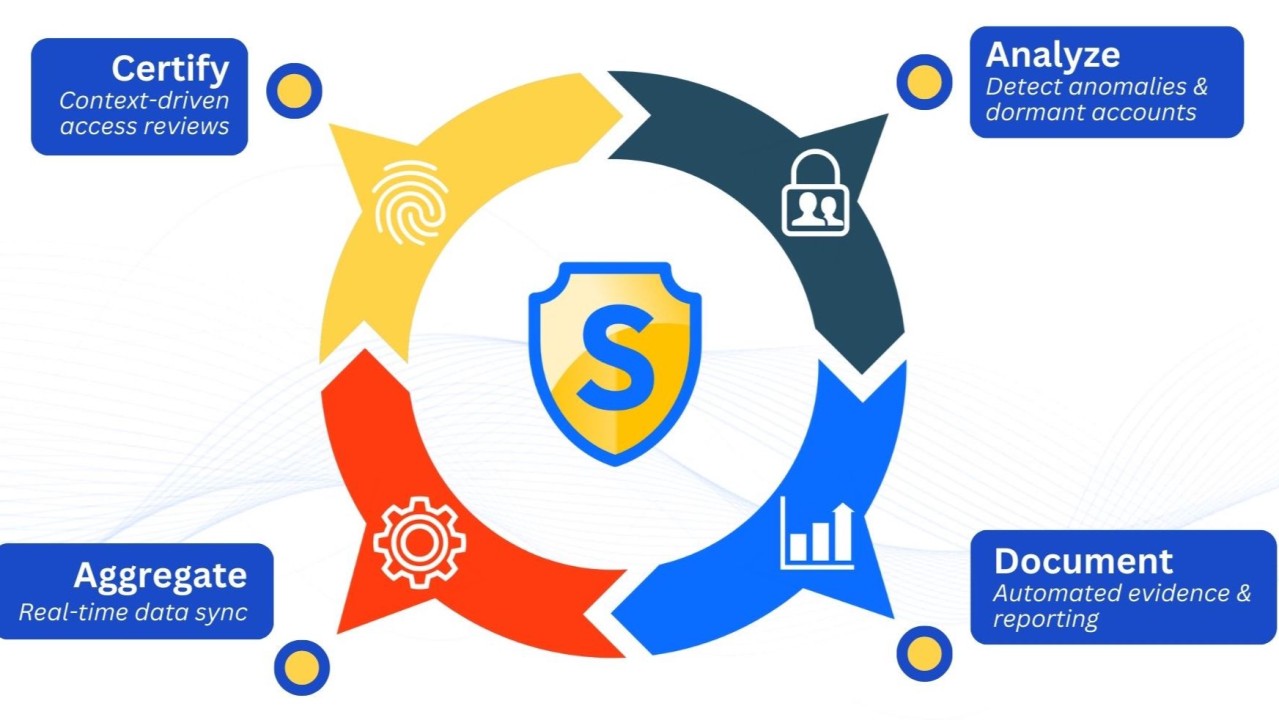
From Manual Audit to Always-On Defense: What ‘Continuous Identity Governance’ Actually Means
Quarterly access reviews are no match for modern threats. Discover what continuous identity governance really means and how it shifts your focus from being audit-ready to truly attack-resistant. Everyone in security talks about automation. The promise of reducing manual toil and eliminating errors is universally appealing. But when it comes to identity governance—the core function…
-

Why Manual Access Reviews Fail Every Quarter (And How to Fix the Cycle)
Quarterly access reviews are a nightmare of spreadsheets and data silos. Discover why this manual cycle fails and how to transform it from a stressful compliance project into a continuous security control. Every single quarter, it’s the same story. Security teams across organizations—from high-growth startups to established enterprises—brace themselves for the same challenge. What should…